Access Control Logs
Overview
Records the history of grants and revocations of server access Direct Permissions assigned to QueryPie users/groups.
Viewing Server Access Control Logs
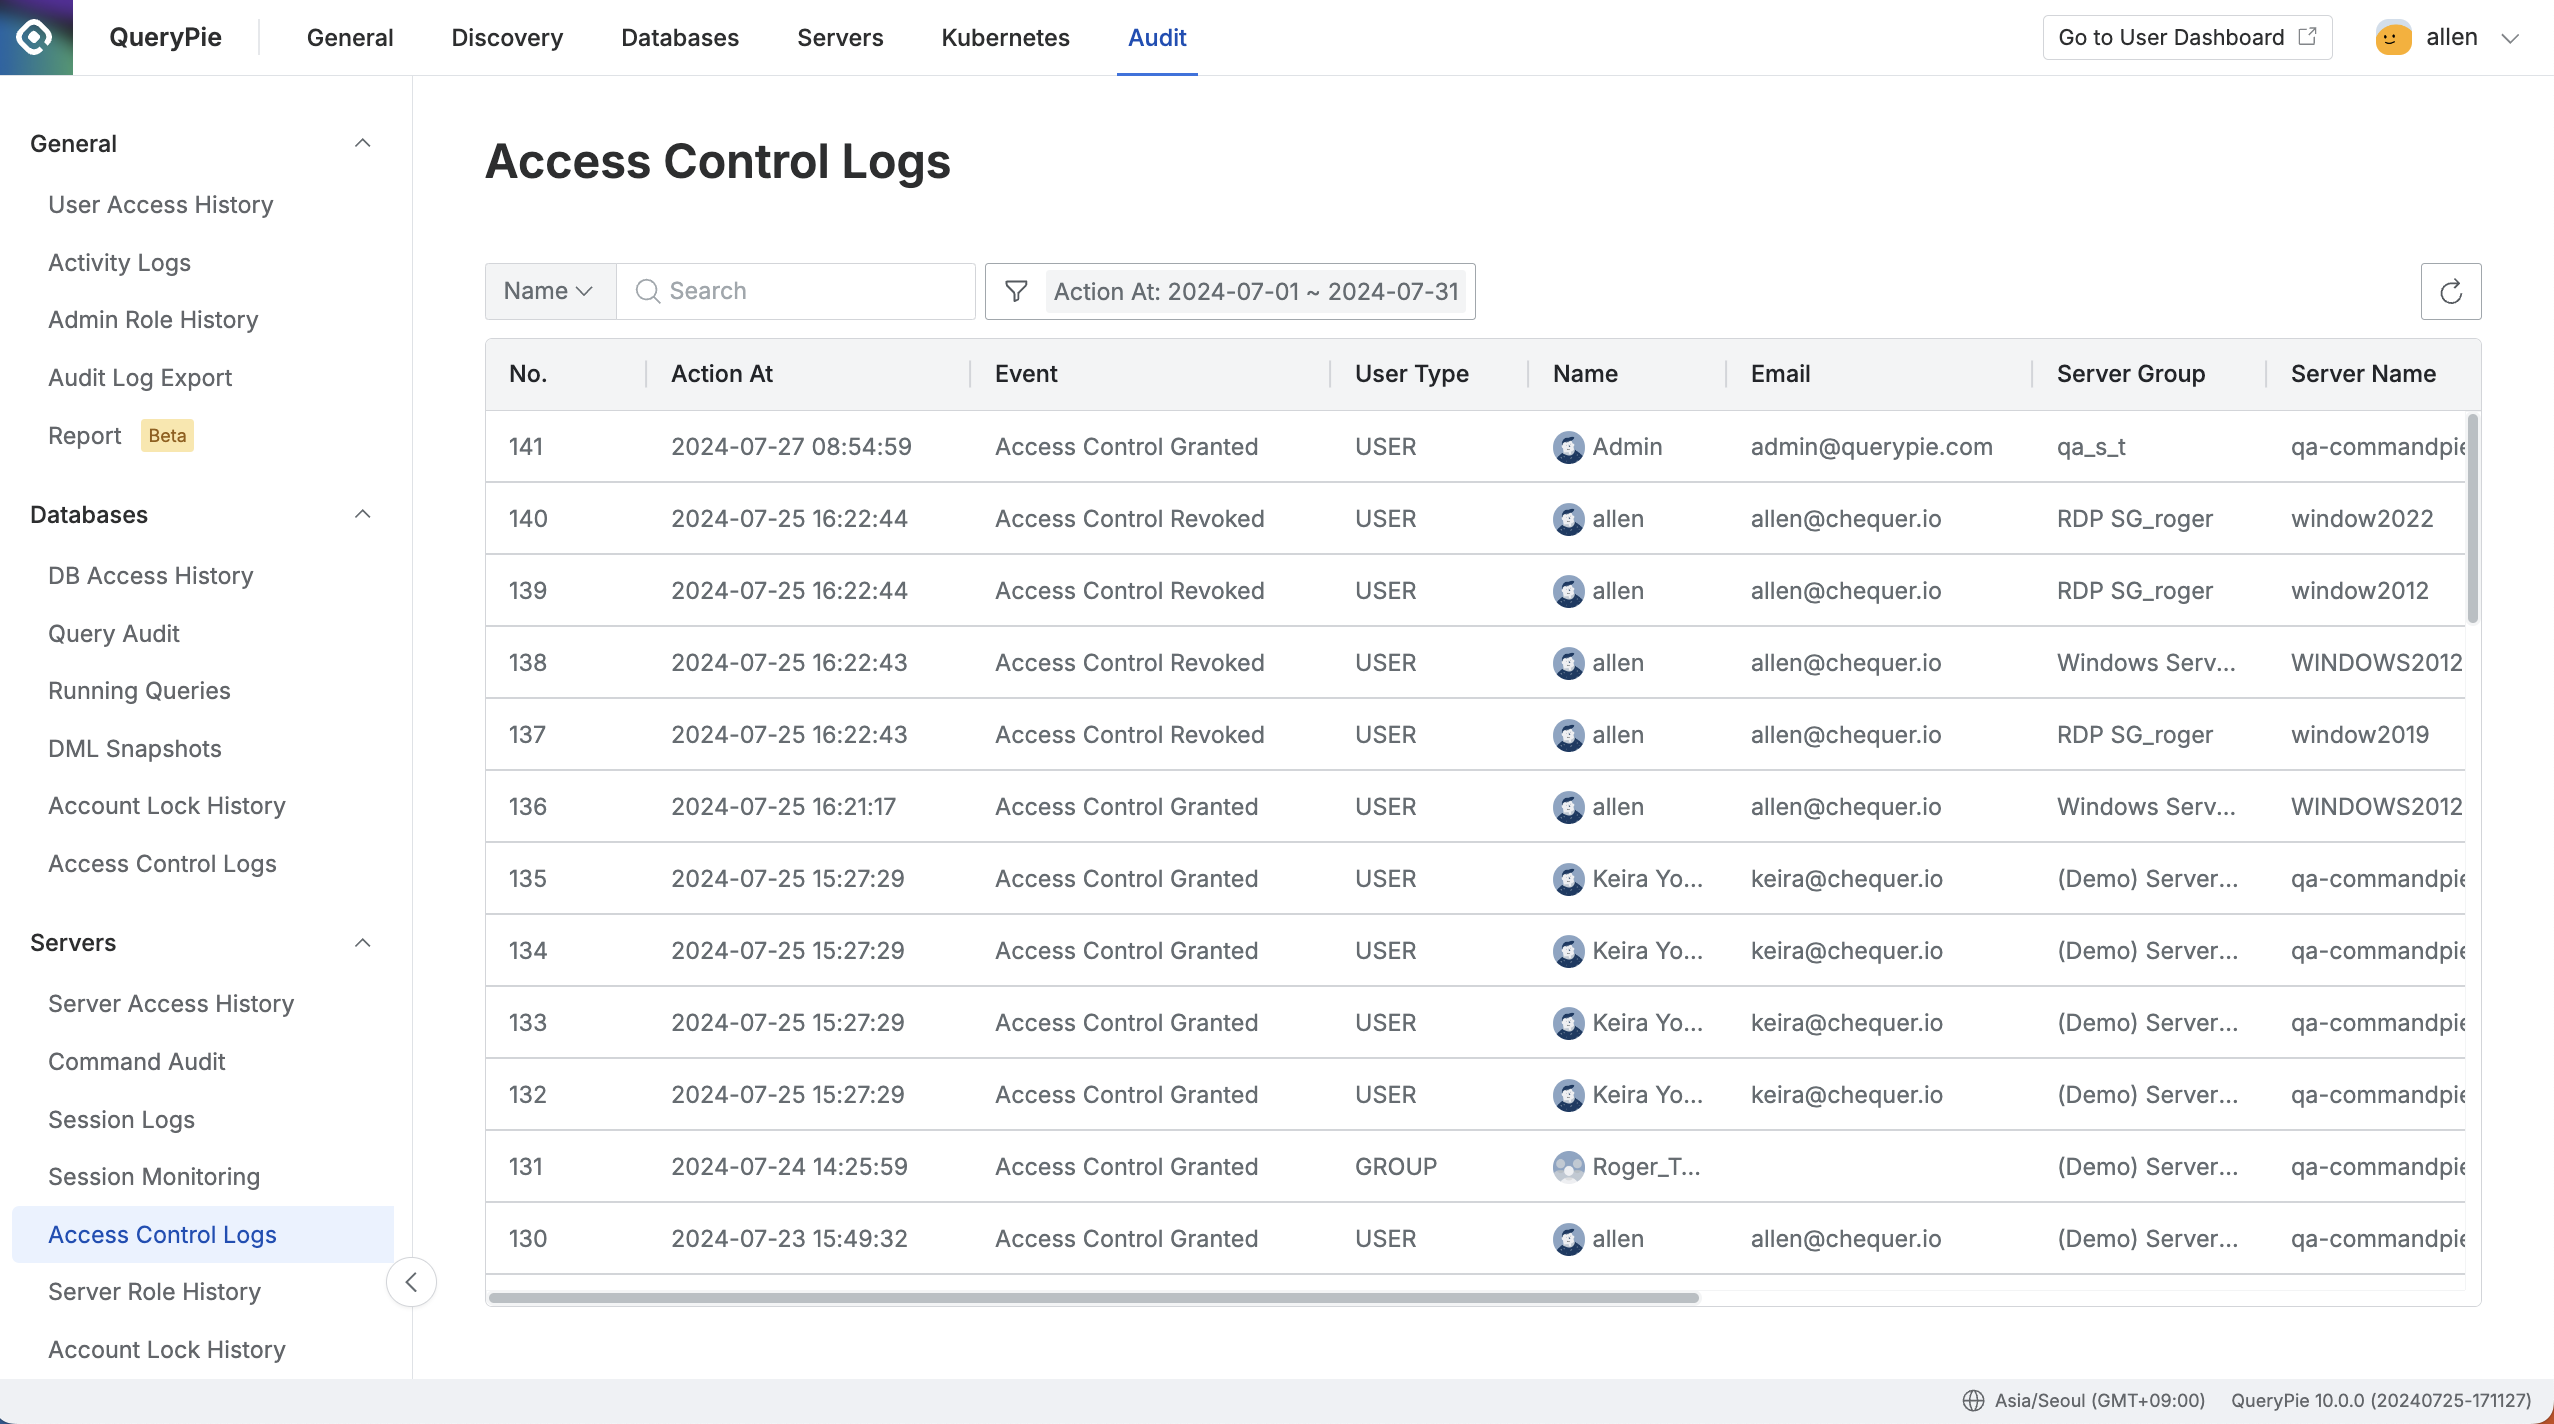
Administrator > Audit > Servers > Access Control Logs
- Navigate to the Administrator > Audit > Servers > Server Access Control Logs menu.
- Logs are displayed in descending order based on the current month.
- You can search with the following conditions through the search field in the top left of the table:
- Name : User name
- Email : User email
- Server Group : Server group name
- Server Name : Server name
- Host : Server host
- Account : Server account
- Click the filter button on the right side of the search field to filter with AND/OR conditions for the following:
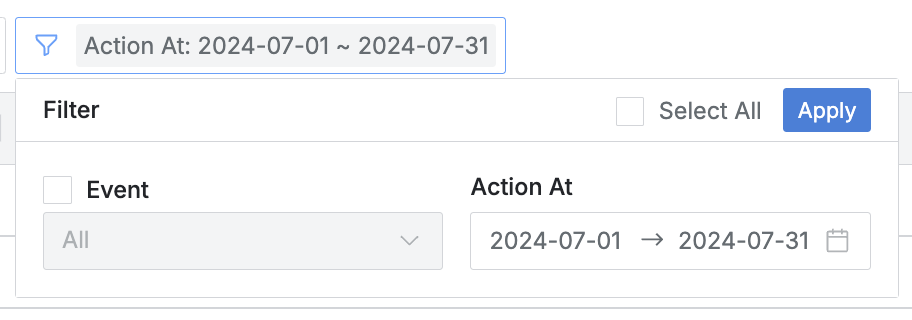
- Event : Event type
- Access Control Granted : Permission grant history
- Access Control Revoked : Permission revocation history
- Whitelist Granted : Command Whitelist grant history
- Whitelist Revoked : Command Whitelist revocation history
- Action At : Permission grant/revocation date and time range
- You can refresh the log list through the refresh button in the top right of the table.
- The table provides the following column information:
- No : Event identification number
- Action At : Permission grant/revocation date and time
- Event : Permission related event
- Access Control Granted : Event where Permission was granted to user/group
- Access Control Revoked : Event where Permission was revoked from user/group
- Whitelist Granted : Event where Command Whitelist was granted to user/group
- Whitelist Revoked : Event where Command Whitelist was revoked from user/group
- User Type : User/group type
- Name : Target user/group name
- Email : Target user email
- Not displayed for groups.
- Server Group : Server group name
- Server Name : Server name
- Host : Server host
- Expiration Date : Permission grant expiration date (scheduled revocation date)
- Account : Server account
- Action By : Administrator name or System who performed the permission grant/revocation
Viewing Server Access Control Logs Details
You can view detailed information by clicking on each row.
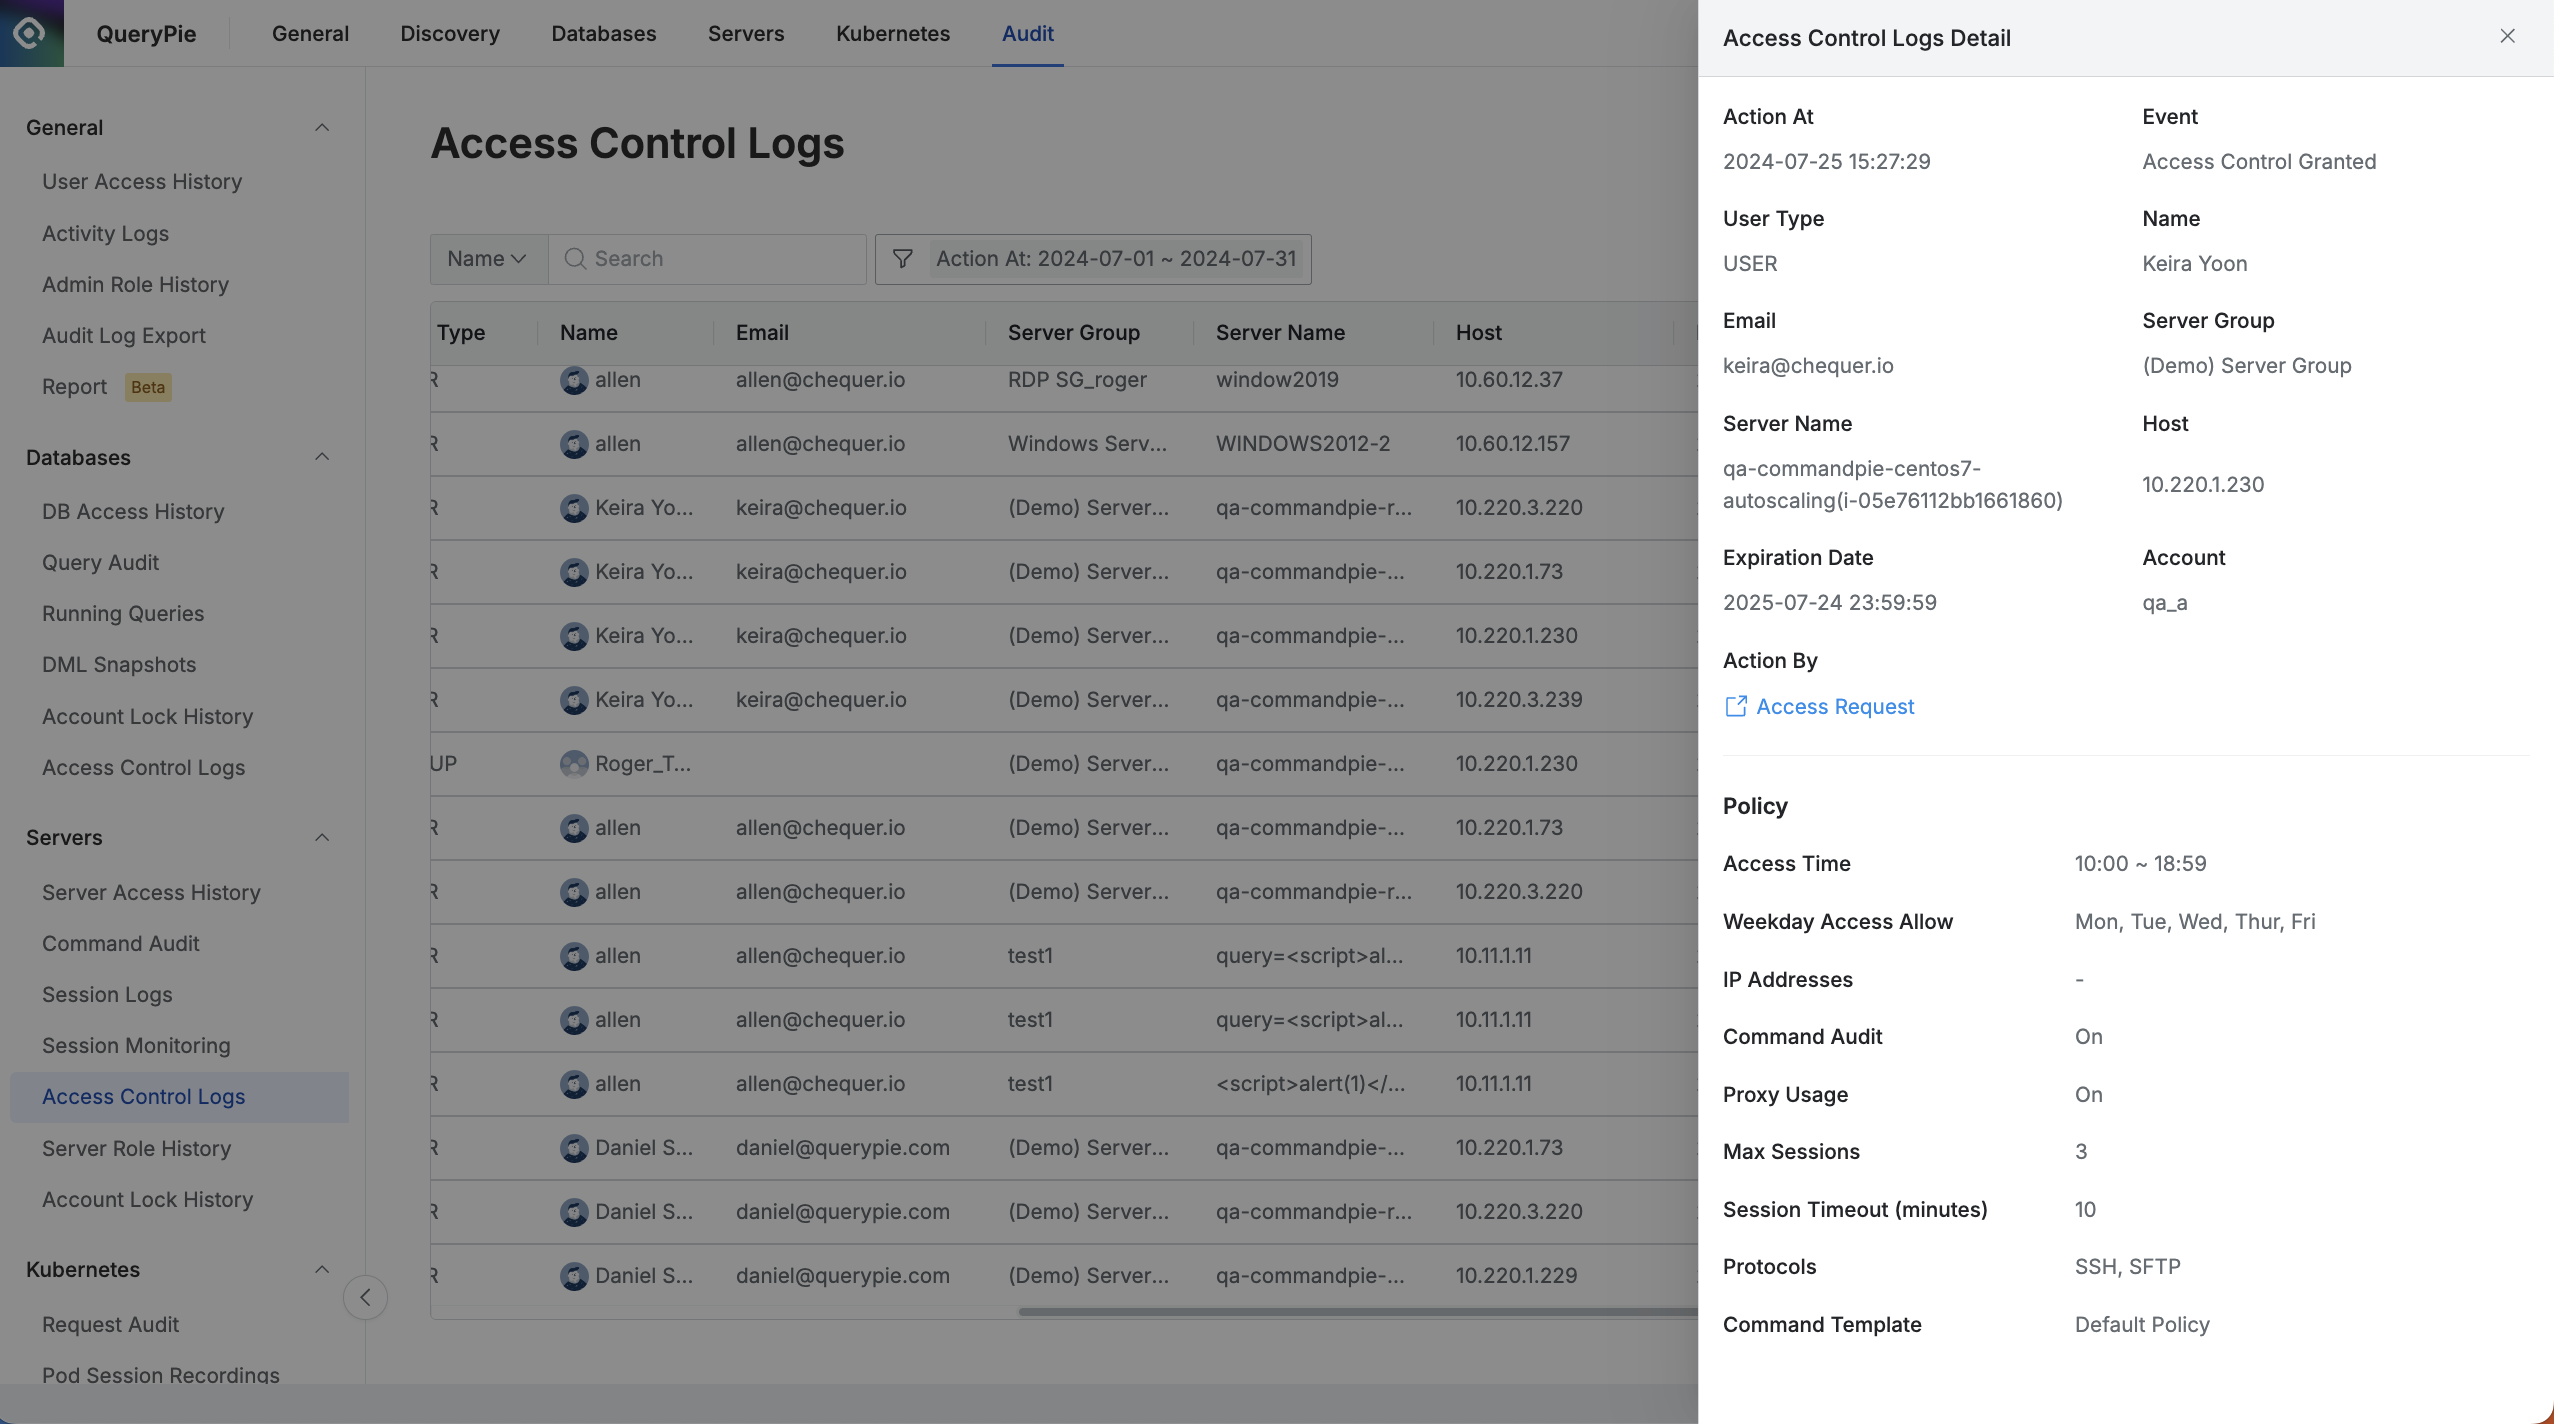
Administrator > Audit > Servers > Access Control Logs > Access Control Logs Detail
- The top displays information based on basic events:
- Action At : Permission grant/revocation date and time
- Event : Event where Permission was granted/revoked to user/group
- User Type : User/group type
- Name : Target user/group name
- Email : Target user email
- Server Group : Server group name
- Server Name : Server name
- Host : Server host
- Expiration Date : Permission grant expiration date (scheduled revocation date)
- Account : Server account
- Action By : Administrator name or System who performed the permission grant/revocation
- The bottom lists policies applied to the granted/revoked Permission:
- Access Control related logs - Policy
- Access Time : Access allowed time
- Weekday Access Allow : Access allowed weekdays
- IP Addresses : Access allowed IP addresses
- Command Audit : Command recording status
- Session Recording: Whether session recording was enabled when the Permission was granted. (Supported from 11.5.8 and 11.6.6)
- Session Recording Max Size (MB): Maximum chunk size of the session recording file applied when the Permission was granted. (Supported from 11.5.8 and 11.6.6)
- Proxy Usage : Access through Proxy (Agent) availability
- Require Privilege : Whether privilege elevation is required
- Allow Local Port Forwarding : Whether local port forwarding is allowed (Supported from 10.3.0)
- Allow RDP Clipboard : Whether RDP clipboard use is allowed (Supported from 11.5.8 and 11.6.6)
- Max Sessions : Maximum number of access sessions
- Session Timeout (minutes) : Session timeout time setting
- Protocols : Access protocols
- Command Template : Applied prohibited command set
- Whitelist related logs - Whitelisted Commands
- Keyword : Exception handling keyword
- RegEx : Exception handling regular expression
- Whitelist Expiration Date : Exception handling expiration date
- Access Control related logs - Policy
Last updated on